AI agent tools run with your permissions. They don't have to.
Every MCP server or agent tool you install today runs as your user. It sees
your SSH keys, your .env files, the whole network. If it misbehaves, you
find out from the damage.
ACT, short for Agent Component Tools, packages a tool as a single WebAssembly component.
The component declares what it needs, this directory and these hosts, and
the host enforces it: undeclared means denied; declared still waits for your
grant. Every decision lands in an audit trail. The same .wasm file is an MCP
server (stdio or Streamable HTTP), a command-line tool, and a browser-tab app.
Try it in your browser
actcore.dev/python is real CPython with numpy and pandas, compiled for WASI (not Pyodide, not Emscripten), executing your CSV inside the tab. It can touch the one file you hand it and reach PyPI, nothing else. Pick the escape example: it asks the component to fetch from a non-PyPI host, and the policy refuses before the request leaves the page.
The first run downloads ~113 MB, once, and needs JSPI: Chrome/Edge 137+ or Firefox 153+. Firefox ships it by default since 153; Chrome Android doesn’t have it yet, so phones are out for now.
Or from a terminal
mkdir -p /tmp/demonpx @actcore/act call actpkg.dev/library/sqlite query \ --args '{"sql":"SELECT sqlite_version()"}' \ --session-args '{"database_path":"/tmp/demo/app.db"}' \ --allow 'fs=/tmp/demo/**'act info <component> shows what a tool can touch before it ever runs.
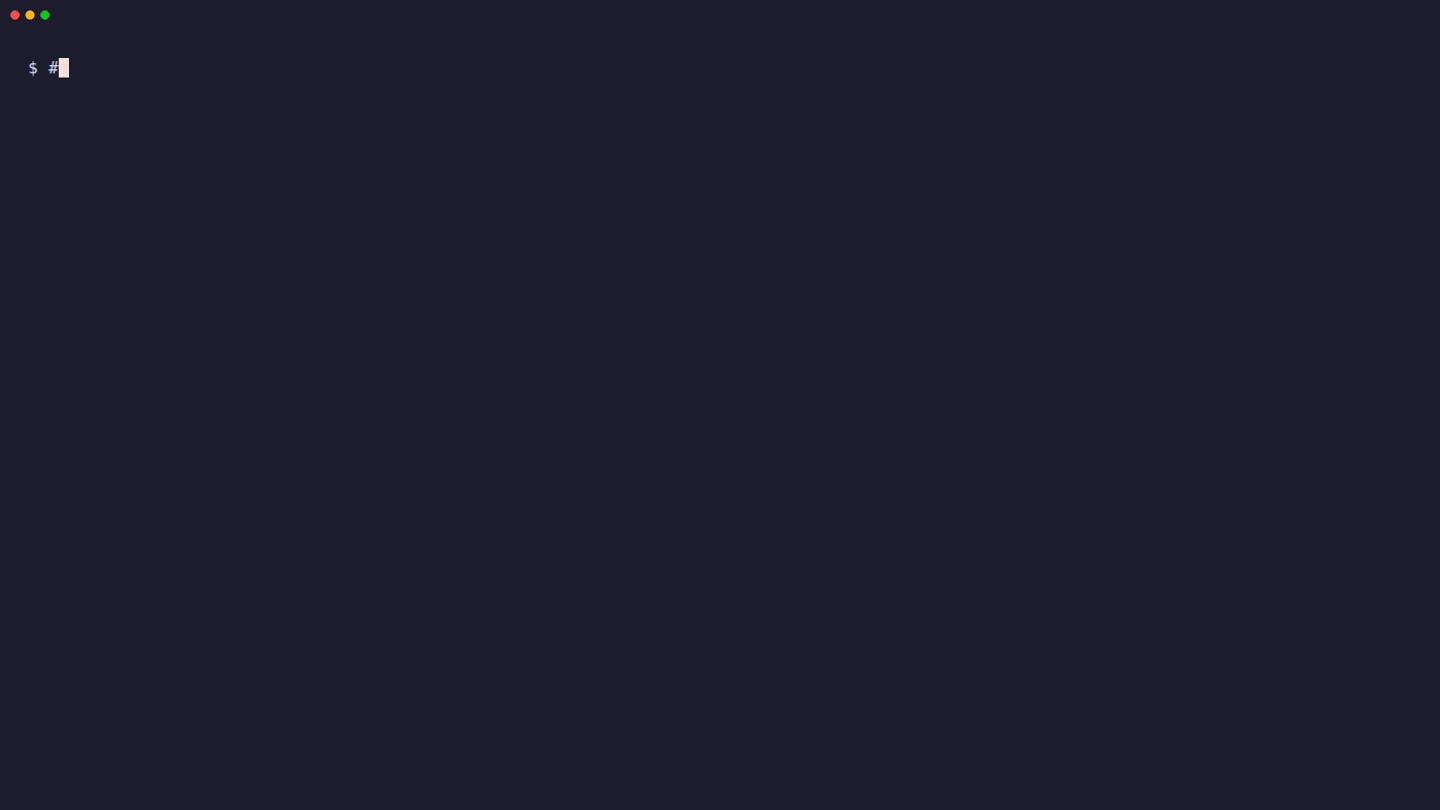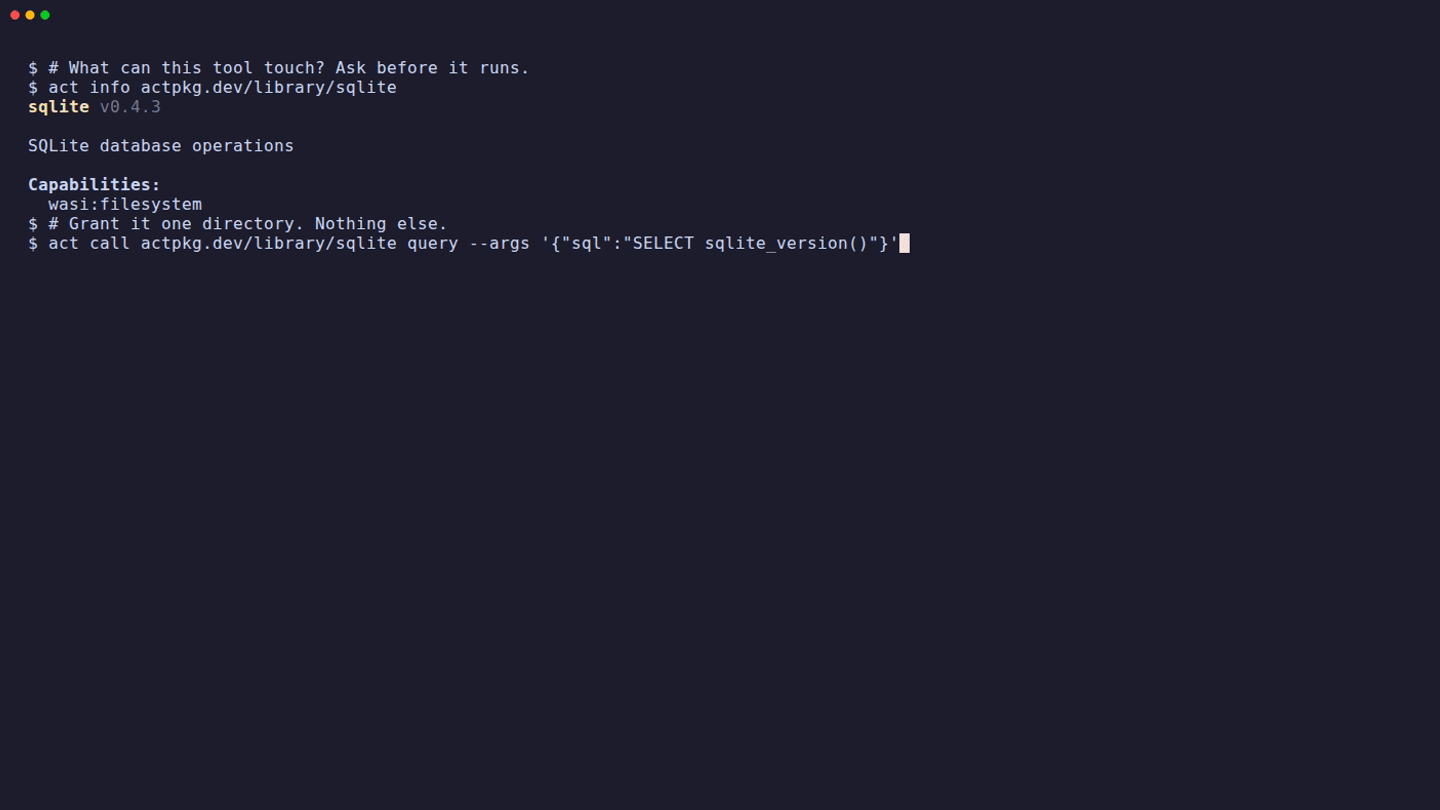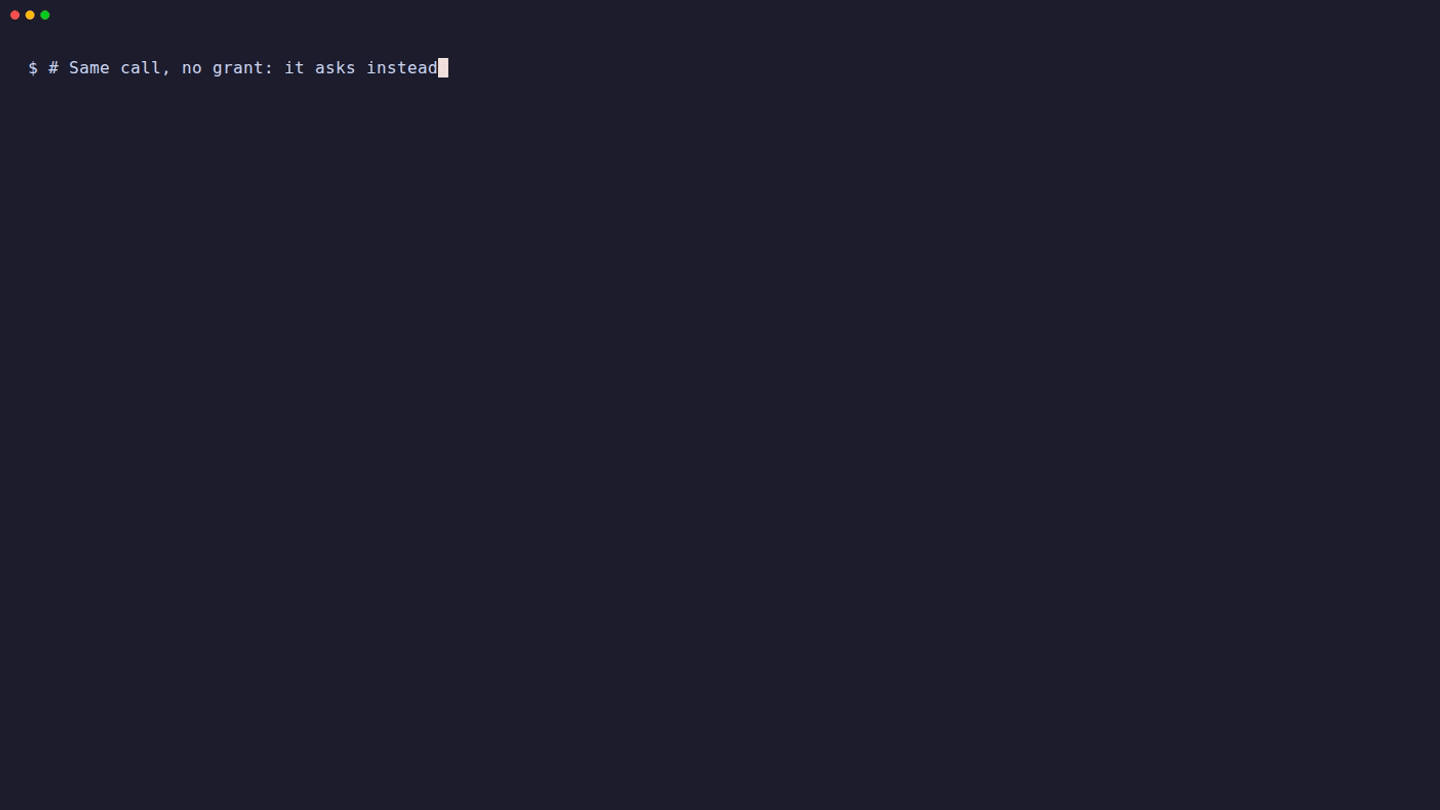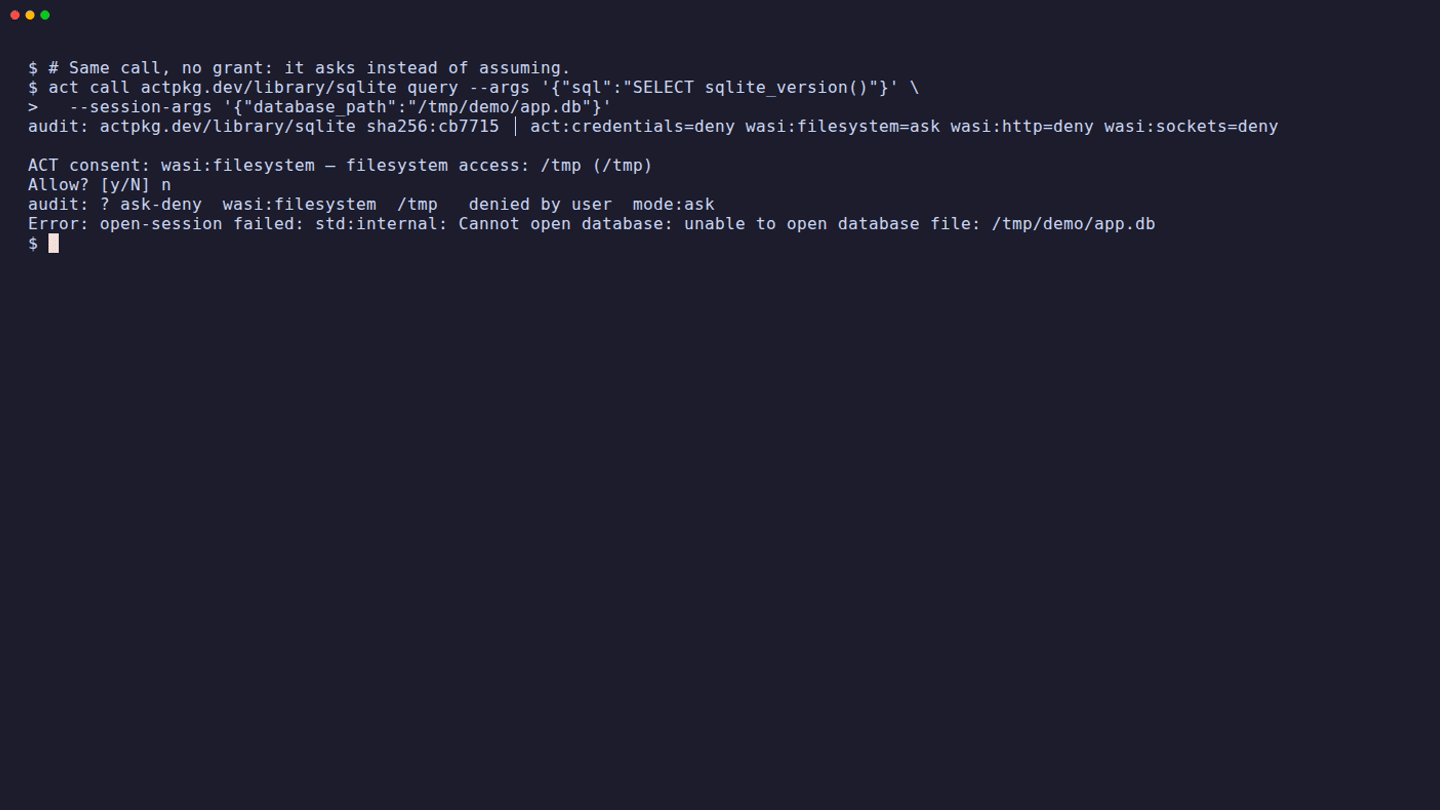
Without a grant, an interactive run asks on first access and a headless
one denies. Every capability decision (allow, deny, ask, and the rule that
decided it) goes to the audit trail on stderr, independently of your logging
setup.
The grant line above is one directory. --allow 'http=https://api.example.com'
is one host. --deny 'fs=/data/secret/**' carves a rule back out. A component
cannot get past what it declared, and you cannot accidentally grant more than
you named.
The ecosystem around it
act, the host: Rust + wasmtime, MCP and CLI, capability policy, audit trail. The current release, 0.14.4, tracks wasmtime 49.0.2 with this year’s engine security advisories closed.act-build: embeds component metadata and pushes to any OCI registry. Published components are signed with keyless cosign in CI.- 23 components on actpkg.dev: sqlite, postgres, http-client, pdf, archive, the Python environment, browser automation over WebDriver BiDi, a VNC desktop.
- Rust and Python SDKs; components in Go, C/C++, Zig, Kotlin and a few more languages run the same way (experimental).
What it isn’t
Not a VM. Isolation is WebAssembly (wasmtime in the CLI, the browser’s own engine in the tab) plus a capability policy on top. A native MCP server has to be rebuilt as a component to get any of this; the SDKs make that a small change, but it is a change.
Feedback wanted
The capability model is the part we’d most like feedback on: what would you need to see before letting a third-party tool run on your machine? The docs cover the policy model end to end, and the code is at github.com/actcore/act-cli (MIT OR Apache-2.0).